


OPINION:
Every day, Americans walk into hospitals and clinics, trusting that the machines monitoring their vital signs produce data that is strictly guarded under doctor-patient confidentiality.
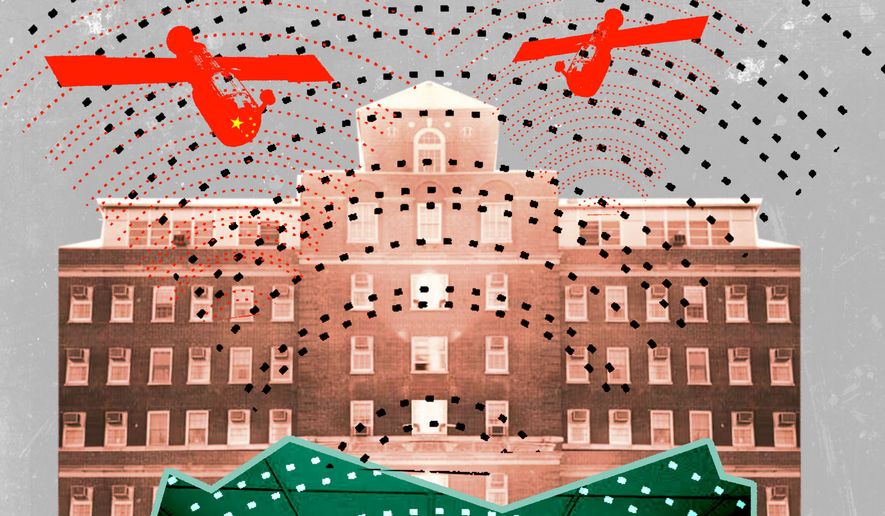
Most have no idea that some everyday medical machines may also be working for and sending data back to Beijing.
In January 2025, the Cybersecurity and Infrastructure Security Agency and the Food and Drug Administration issued a joint warning about Contec CMS8000 patient monitors manufactured in Qinhuangdao, China.
People were interested in these podcasts
The agencies found three distinct cybersecurity vulnerabilities. One allowed unauthorized users to remotely control the device. Another contained a backdoor that could transmit patient data, including personally identifiable information and protected health information, to overseas servers. A third allowed outside actors to access and potentially manipulate the device in ways that could affect treatment decisions physicians rely on in life-or-death situations.
Backdoors are ubiquitous in Chinese equipment because Chinese law requires them. China’s 2017 National Intelligence Law compels every Chinese company and its subsidiaries, without exception, to cooperate with the Chinese Communist Party’s intelligence apparatus on demand, in secret. There is no independent court review or transparency when data handover occurs.
This legal requirement for espionage often ends up coded into the firmware of Chinese devices. Effectively, there is no such thing as a private Chinese company that operates outside party reach. So when a Chinese-owned or -manufactured medical device connects to an American hospital network, the CCP has a seat at the table.
Texas Gov. Greg Abbott has decided that is unacceptable. Earlier this year, he issued a formal directive to the Texas Health and Human Services Commission and other state health agencies to immediately review and mitigate cybersecurity risks associated with Chinese-manufactured patient-monitoring devices.
Mr. Abbott’s directive came on the heels of a letter from 53 Texas state legislators demanding a total purge of CCP-linked technology from hospital rooms. The legislators called for strict cybersecurity procurement standards, a full audit of existing state contracts and incentives to build domestic manufacturing alternatives.
Florida is building momentum as well. Attorney General James Uthmeier subpoenaed medical technology company Contec over its data protection practices, subpoenaed camera company Lorex in a data privacy probe and later sued router maker TP-Link over security and allegations of ties to China.
In February, he launched the CHINA Prevention Unit, a dedicated division within the Office of the Attorney General focused on foreign adversary threats to Florida consumers, patient data and economic security. Mr. Uthmeier directed the unit to demand audits from nine additional Chinese-owned medical device companies operating in the state, including Mindray North America and United Imaging.
Sen. Rick Scott, Florida Republican, put the stakes plainly in a recent RealClearPolitics op-ed, writing, “American patients deserve to have confidence that the medical machines watching over them in vulnerable moments belong to American doctors and hospitals, not Beijing.”
The federal government is moving too. The Department of Commerce has opened a Section 232 national security investigation into the risks posed by foreign-made medical devices, including the potential for foreign actors to weaponize devices already installed in American healthcare facilities.
The threat is growing faster than the policy response, and the numbers make that plain. In 2025, Chinese medical device giant Mindray reported that its international revenue surpassed its domestic revenue for the first time**, with international expansion — particularly in Europe — driving much of that growth**.
The company now covers approximately 80% of integrated delivery network hospital systems in the U.S. In 2025, United Imaging, another Chinese-owned manufacturer, reported revenue growth of nearly 34% on the strength of its global push.
These companies are systematically embedding themselves into the core infrastructure of American healthcare — in operating rooms, intensive care units and imaging centers — while remaining legally obligated to cooperate with Beijing on demand.
The investigation deserves urgency, but states need not wait for Washington to finish its review. States can prevent Medicaid funds from flowing to entities that purchase Chinese-made medical devices. They can direct purchasing boards to restrict funding for Chinese technology. They can pass laws that enhance state penalties for foreign medical data espionage and incentivize domestic alternatives.
They can even prohibit the use of certain equipment in state-licensed healthcare facilities, as several states did to ban sanctioned Chinese genetic sequencing devices in their healthcare systems.
Protecting patient data from a foreign adversary is a core function of state government. Governors, legislatures and attorneys general each have a role to play in securing vital American healthcare data from our foremost adversary.
• Michael Lucci is founder and CEO of State Armor.

Please read our comment policy before commenting.